Identity, architected.
We build and advise on identity for medium sized organizations through very large enterprise and government, so one user is one identity across every line of business.
Book a scoping callMost organizations do not have an identity problem. They have several, spread across business units that each solved it their own way. We help you control the many identities a single user accumulates, from defining the policies your organization runs on to deploying on-premises identities into the cloud.
Identity management with MIM and SailPoint
We use Microsoft Identity Manager (MIM or FIM) or SailPoint IdentityIQ to break organizational data silos and aggregate them into a central store, which then serves authentication for applications while staying compliant with the regulators' requirements.
We work in both products, which is why we are able to migrate organizations off MIM to SailPoint IdentityIQ. That is our main offering, and it has its own page: MIM to SailPoint IdentityIQ migration.
Okta to Entra ID migration
We have moved organizations off Okta to Entra ID. The discipline is the same one we apply to MIM: establish what the current system actually does, prove the new one matches it, then decommission the old one.
That order matters. An Okta tenant accumulates sign-on policies, group rules, network zones, and application assignments that nobody documented at the time. Rebuilding from an assumption about what those do is how a migration quietly loses behavior. Rebuilding from what they demonstrably do is how it does not.
Microsoft Entra ID
Entra ID is the gatekeeper of your assets in the cloud. We design and implement Entra ID at scale, and we support it afterwards.
We use Microsoft Entra Connect to synchronize your on-premises Active Directory to Entra ID securely, so a single identity represents a user from on-premises through to the cloud.
MFA and self-service password reset
We use Microsoft MFA to secure access to Entra ID, applied to users through conditional access rather than blanket policy. MFA combined with self-service password reset also cuts the volume of password change calls reaching your helpdesk.
Conditional access is where the two meet. We set the policies that decide which users, on which devices, from which locations, get challenged and for what.
Passwordless
If a password exists, it is an attack surface. We can get you to a readiness state for passwordless sign-in using a security key or the Microsoft Authenticator app.
That covers FIDO2 security keys, Windows Hello for Business, and Microsoft Authenticator, with the rollout sequenced so users are not locked out of their own accounts partway through.
AD FS to Entra federation
We can move you from on-premises AD FS to Entra federation and everything that entails: relying party trusts, claim rules, certificate lifecycles, and the applications that depend on them.
Modern authentication
Moving your applications to modern authentication using OpenID Connect and OAuth 2.0, off Windows NTLM, LDAP, and Kerberos. Single sign-on across the estate, rather than one credential prompt per application.
Azure Key Vault
Azure Key Vault protects and secures your secrets: API keys, certificates, and credentials. It improves application security directly, because credentials stop living in application configuration files where anyone with source access can read them.
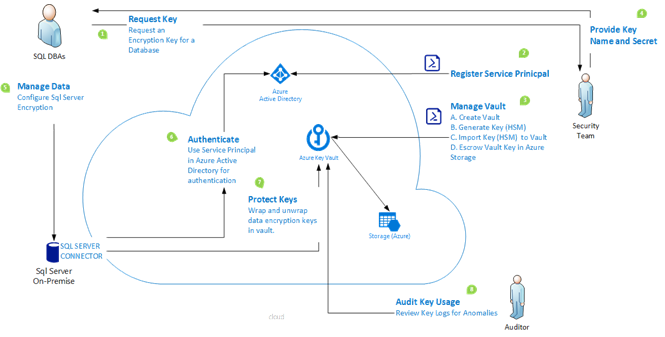
Below is the key management flow from a SQL Server transparent data encryption implementation we built. A database administrator requests an encryption key, the SQL Server connector authenticates to the directory with a service principal, keys are wrapped and unwrapped inside the vault rather than handed out, the vault key is escrowed to storage, and an auditor reviews key usage logs for anomalies. Nobody in that diagram ever holds the key material.
Security architecture
Network security groups and Azure Firewall are among the tools we use to secure Azure infrastructure by restricting access to resources.
We also use identity governance entitlements and access reviews to streamline access control, so entitlements are granted through a defined process and reviewed on a schedule instead of accumulating forever. Alongside that we use the monitoring, auditing, and alerting capabilities of Entra ID, because a control you cannot observe is a control you cannot evidence.
Microsoft 365, Teams, and licensing
Setup and configuration for Microsoft 365 and Teams, licensing assignment and review, and the conditional access policies that govern access to both.
Still running MIM?
Book a scoping call. We will tell you what your migration actually involves, before you commit to anything.
Book a scoping call